Mobile Phone Forensics: Extraction and Analysis for Attorneys, Investigators and Law Enforcement
A mobile phone is often the most complete record of who a person was in contact with, what was said, and where they were. Gillware’s mobile phone forensics service preserves, extracts and analyzes that data for attorneys, law enforcement agencies and corporate investigators, with every step documented so the work can be reviewed, explained and repeated.
Need a phone examined for a case?
Before anyone charges, unlocks or browses the device, talk with our forensic team about preservation, authority and scope. The consultation is free.
This page is written for the people who engage a forensic examiner: prosecutors and defense counsel, civil litigators, corporate counsel and HR investigators, and the agencies and investigators who work with them. It explains what an examination can show, who we take on (and who we don’t), how to preserve a phone before it reaches us, how extraction and analysis work, and how to start a case. If you are not sure whether your matter calls for forensics or for data recovery, our page on digital forensics vs. data recovery explains the difference. If your own phone is broken and you simply need your photos and files back, see our phone data recovery services instead.
What a mobile forensic examination can show
What can be extracted depends on the phone, its operating system version, its condition and its lock state, and on what the legal authority for the examination allows. Within those limits, a phone can hold:
- Call history and contact lists
- Text, multimedia and app-based messages, with timestamps and participants
- Photos, videos and audio, often with the date, time and device information recorded when they were made
- Location artifacts, such as photo metadata, saved places, Wi-Fi connection history and app location records
- Web browsing and search history
- Calendar entries, notes and documents
- Data stored by installed apps, including messaging, social media and cloud storage apps
- Account and synchronization records that point to other devices and cloud services
- System logs and usage records that show when the device was used, unlocked, reset or connected
Deleted data is a separate question. On a modern, encrypted iPhone or Android phone, permanently deleted content is often unrecoverable from the device itself, although traces of a deletion, older copies in app databases, backups and synced devices can still matter to a case. Our page on deleted text messages and contacts explains why in plain terms. We tell you at the scoping stage what is realistic for the specific device, so the examination is planned around what the phone can actually provide.
Who engages us, and who we don’t take on
Gillware has supported digital forensics work for law enforcement, law firms and businesses since 2016, using many of the same tools and techniques our data recovery lab developed for damaged devices. Mobile forensics engagements typically come from:
- Law enforcement agencies and prosecutors examining a device under a warrant, consent or other lawful authority.
- Defense attorneys who need an independent examination or a review of the extraction and analysis performed by another examiner.
- Civil litigators preserving and examining devices in disputes where messages, photos or location records are at issue, under a court order, agreement of the parties or other proper authority.
- Corporate counsel, HR and compliance teams examining company-owned devices in employee departures, misconduct inquiries and employment disputes, where the company has the right to examine the device.
Deleted messages and contacts: law enforcement and attorneys only
We want to be plain about this. Gillware performs deleted text message and deleted contact work only for law enforcement agencies and for attorneys acting under a court order or other proper legal authority, where the chain of custody is documented and the work is part of a legitimate legal process. We do not take on private requests to read another person’s messages. That includes people who suspect a partner of cheating and parents who want to read a child’s messages. Accessing someone else’s communications without consent can be illegal, and the legal questions are serious even when the phone is on a family plan. If that is your situation, we would rather tell you now than take your money. If you believe a crime has been committed, the right first call is to law enforcement or an attorney.
Preserving the phone before it reaches us
The first hours after a phone is collected decide how much of it can be examined later. Phones keep changing while they are on and connected: messages arrive, apps clean up their own data, automatic updates install, and a remote wipe command can erase everything. These are the general steps we recommend; your agency’s or firm’s own procedures come first.
- Don’t browse the phone. Opening apps or scrolling through messages changes the data and can be challenged later. Record what is on the screen with a photograph if you must, and stop there.
- Cut it off from networks. If the phone is on, isolate it from cellular, Wi-Fi and Bluetooth (airplane mode, if you can set it without exploring the device, or a signal-blocking bag), so it can’t receive new data or a remote wipe.
- Keep it charged if it is on. A phone that is unlocked or has been unlocked since it last started can be in a more accessible state than one that has been switched off and restarted. Ask us before you let the battery run down.
- Leave it off if it is off. Don’t power on a phone that is off, and don’t charge a phone that is wet, swollen or burned.
- Don’t guess passcodes. Repeated wrong attempts can lock the device for long periods or trigger a setting that erases it.
- Write down what you know. Passcodes or patterns lawfully provided, the accounts the phone uses, other devices it syncs with, and where and when it was collected.
- Start the custody record now. Note who collected the phone, when, and every hand-off since, and keep the legal authority for the examination with the case file.
How we extract data from a phone
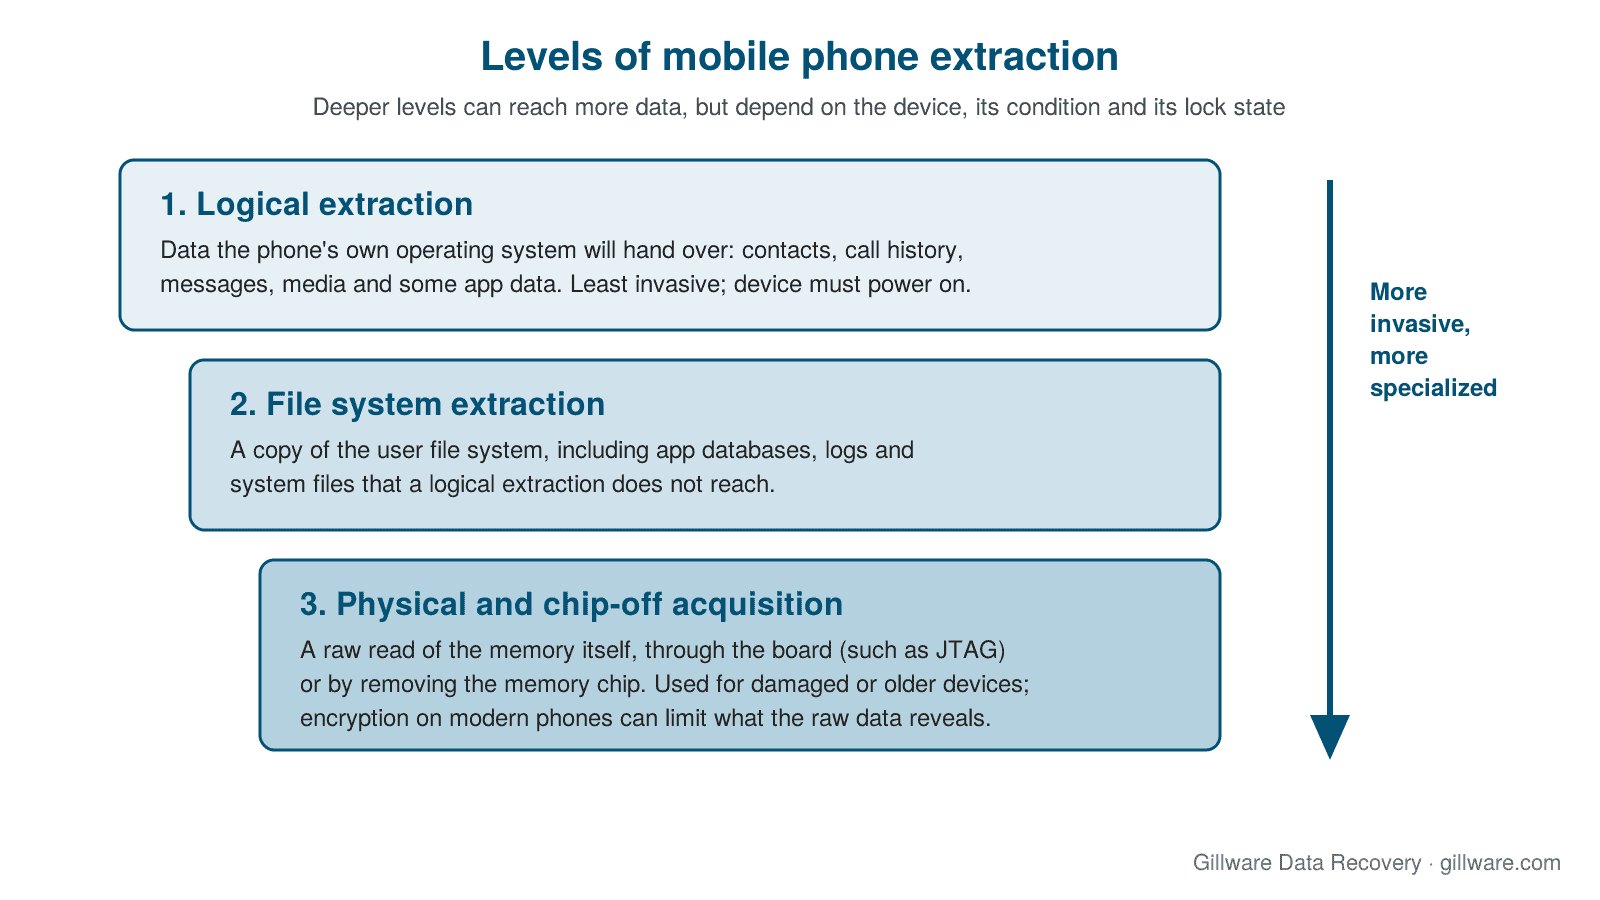
Forensic extraction happens at different levels. The examiner chooses the method that fits the device and the questions in the case, starting with the least invasive approach that can answer them.
Scoping a mobile forensics matter? Book a free consultation to talk through devices, authority and deadlines.
Logical extraction
A logical extraction collects the data the phone’s own operating system will provide through its normal interfaces: contacts, call history, messages, media and some app data. It is the least invasive method and is often enough for focused questions, but it depends on a working, accessible device and does not reach everything stored on the phone.
File system extraction
A file system extraction copies the user file system, including the databases that apps use to store messages and records, along with logs and system files a logical extraction does not reach. This is often where the most useful detail in a case is found, such as timestamps, app activity and traces of deletion.
Physical and chip-off acquisition
When a phone is damaged, will not power on, or cannot be accessed through its normal interfaces, the memory itself may need to be read. Depending on the device, that can mean reading the memory through test points on the circuit board (see our JTAG forensics page) or removing the memory chip and reading it directly, as described on our chip-off forensics page. These methods are invasive and specialized, and on modern phones with hardware-backed encryption the raw memory may not be readable without the device’s own keys. We explain those limits during scoping, before any invasive step is taken.
Damaged and destroyed phones
Phones arrive water-damaged, burned, crushed and deliberately broken. Our engineers have spent more than two decades recovering data from failed and damaged storage, and the same board-level and memory skills our data recovery lab uses on damaged phones are applied in forensic cases, with the custody and documentation requirements of a forensic examination. Work that needs a clean environment is done in our ISO 5 (Class 100) cleanroom.
Chain of custody and documentation
An examination is only as useful as the record behind it. From the moment a device arrives, every step is documented so another qualified examiner could review it and repeat it.
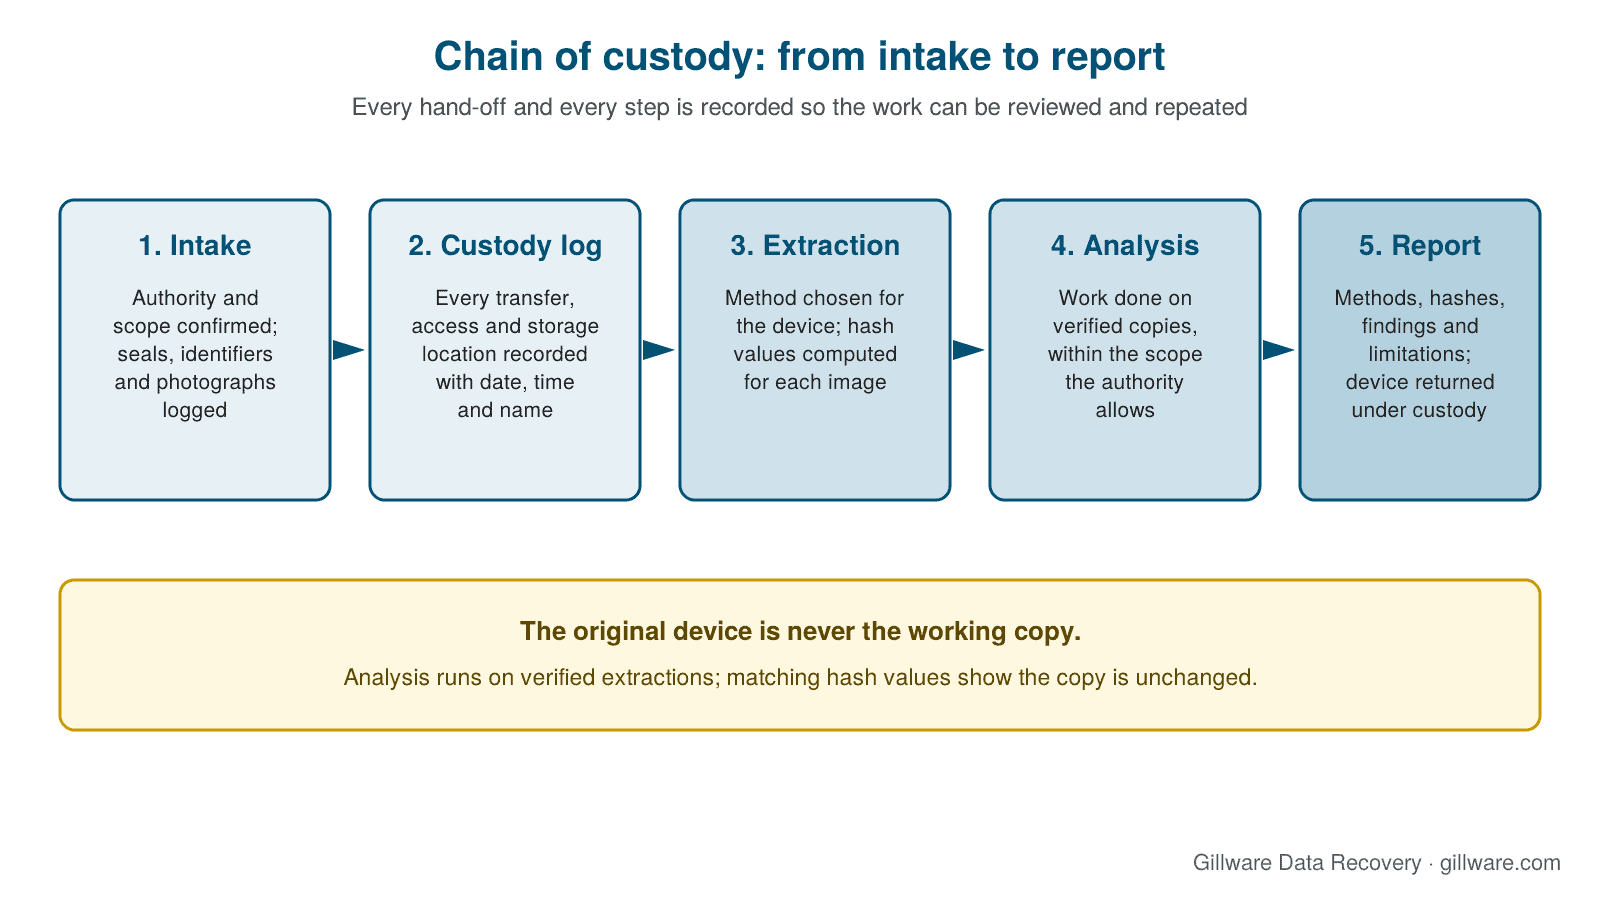
- Intake. We confirm the legal authority and the scope of the examination, then record the device’s condition, identifiers and seals, with photographs.
- Custody log. Every transfer, access and storage location is recorded with the date, time and the person responsible. Devices are held in a secured facility; our security page describes how we protect client data and devices.
- Verified copies. Each extraction is hashed when it is created, and analysis runs on working copies. Matching hash values show that the data examined is the data extracted.
- Examiner notes. Methods, tool categories and versions, settings and any problems encountered are written down as the work happens, not reconstructed afterward.
- Return. The device and any original media go back under the same custody procedures, along with a record of everything that was done to them.
Analysis and reporting
Analysis is shaped by the questions in the case and limited to what the legal authority allows. A warrant, court order or agreement may restrict the examination to certain dates, contacts or types of data, and we work inside those limits. Our reports are written to be read by attorneys, investigators and courts, not just by other examiners. A typical report sets out what was received and in what condition, the methods used, hash values, the findings tied to the specific records that support them, and the limitations of the examination. Where a matter requires it, our examiners can explain their methods and findings in testimony.
We don’t promise outcomes. Whether evidence is admitted is for the court to decide, and an examiner’s job is to report what the data shows, including what it doesn’t show. What we can promise is careful, documented work that can stand up to scrutiny from the other side.
Locked and encrypted phones
Modern iPhones and Android phones encrypt their storage and tie it to the device passcode. Whether a locked phone can be examined, and how deeply, depends on the model, the operating system version, whether the phone has been unlocked since it last started, and what the legal authority provides for. Sometimes the answer is a full file system extraction; sometimes it is limited to what the phone exposes while locked, or to backups and synced accounts the authority covers. We tell you which situation you are in before work begins, and we don’t take on work we can’t do properly.
Forensic services by device
- Cell phone forensics
- Android forensics
- Smartphone and iOS forensics
- Samsung forensics
- Chip-off forensics and JTAG forensics
- Mobile malware and spyware examinations
Starting a case
Every case starts with a free consultation, and you approve all recovery fees in writing before any recovery work begins. On the call we will ask about the device and its condition, the legal authority for the examination, the questions you need answered, and your deadlines, and we will tell you plainly what is realistic. If the device needs to come to our lab in Madison, Wisconsin, we agree the shipping and custody arrangements before anything ships.
Why Gillware
Gillware has spent more than two decades recovering data from failed and damaged storage, and since 2004 we have recovered data from more than 100,000 storage devices. More than 1,500 IT professionals refer their clients to us. That recovery background matters in forensic work: phones that other examiners can’t read because they are damaged, wet or destroyed are the devices our engineers work on every day, and our forensic work adds the documentation, custody and reporting discipline a legal matter requires.
Mobile phone forensics FAQ
Can you get into a locked phone?
Sometimes. It depends on the phone model, its operating system version, its state when it was collected and the legal authority for the examination. We assess this during the consultation and tell you what is realistic before any work begins.
Can you recover deleted text messages?
For law enforcement agencies and for attorneys acting under a court order or other proper legal authority, we examine phones for deleted messages and the traces they leave. On modern encrypted phones, permanently deleted content is often gone from the device itself, but app databases, backups and synced devices can still hold relevant records. We do not take on private requests to read someone else’s messages.
Will the evidence be admissible in court?
Admissibility is for the court to decide, and no honest examiner can guarantee it. We document every step, from intake and custody through extraction, hashing and analysis, so the work can be reviewed and repeated by another qualified examiner.
The phone is broken or water-damaged. Can it still be examined?
Often, yes. Our data recovery engineers work on damaged phones every day, and the same skills are applied in forensic cases under custody. Don’t power on or charge a wet or damaged phone; call us first.
Can you review another examiner’s work?
Yes. Attorneys engage us to review extraction reports and the methods behind them, or to perform an independent examination of the same device where the authority allows.
How do we get started?
Call 877-624-7206 or book a free consultation. We will talk through the device, the legal authority, the scope and your deadlines, and agree the custody arrangements before anything ships.
Have a phone that matters to your case? Let’s talk first.
Our highly experienced engineers strive for the highest success rates in the industry. Talk with one of our enterprise storage engineers before anything else is done to the system.
- Free technical consultation with one of our enterprise storage engineers
- A written recovery agreement before work begins
- No billing surprises: you approve all recovery fees in advance
- Emergency service for business-critical downtime